See what attackers see. Fix it before they act.
Agents find the internet-facing systems tied to your domain, subsidiaries included, then exploit them the way an adversary would: real attacks, chained into proven paths. Each path comes with a fix, and a retest to confirm it’s closed.
From the open internet
to a closed path
Discover
Start with one domain. Agents find related domains, subdomains, IPs, ports and services, with an ownership-confidence score and supporting evidence for each asset.
Get a demo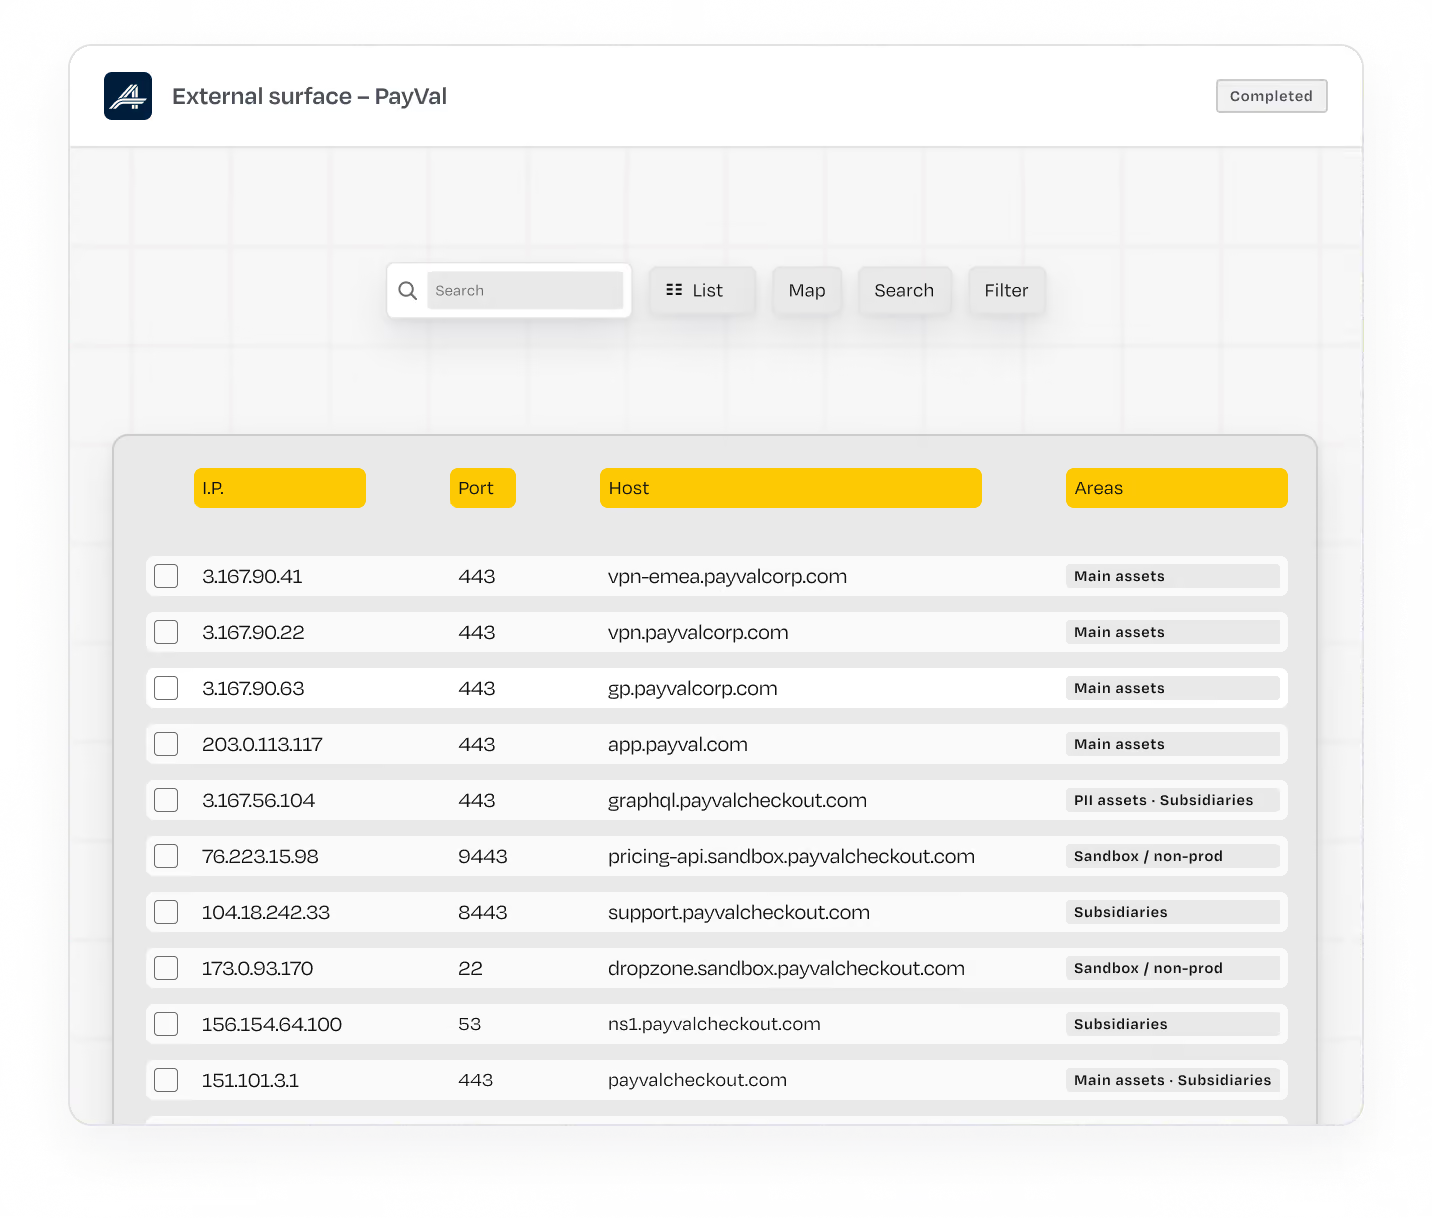
Plan
Agents build an attack plan for each type of exposure, using leaked-credential intelligence and any pentest, bug bounty or ASM context you provide. You approve the plan before attacks run.
Get a demo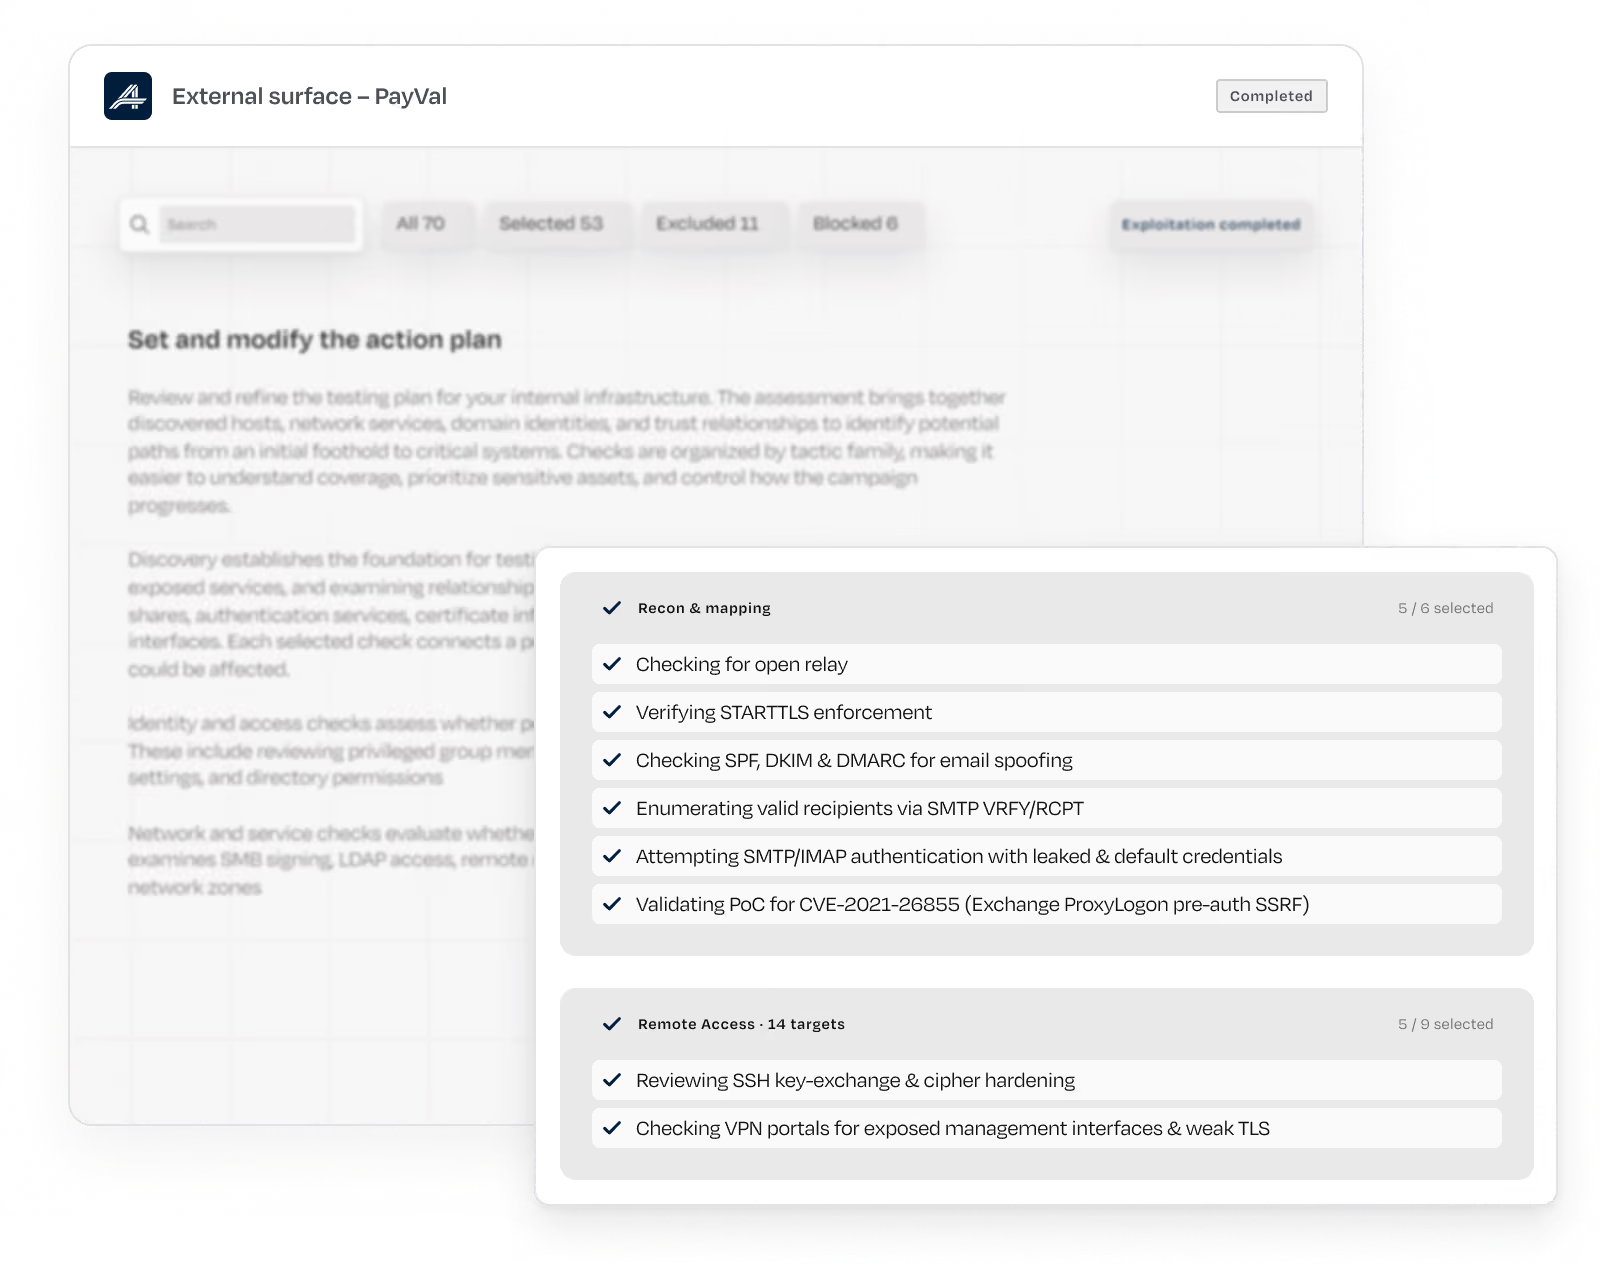
Exploit
Agents attack web apps, APIs, VPN gateways, mail servers and other exposed services, chaining weaknesses into verified paths. Every reported path must reproduce, with its blast radius attached.
Get a demo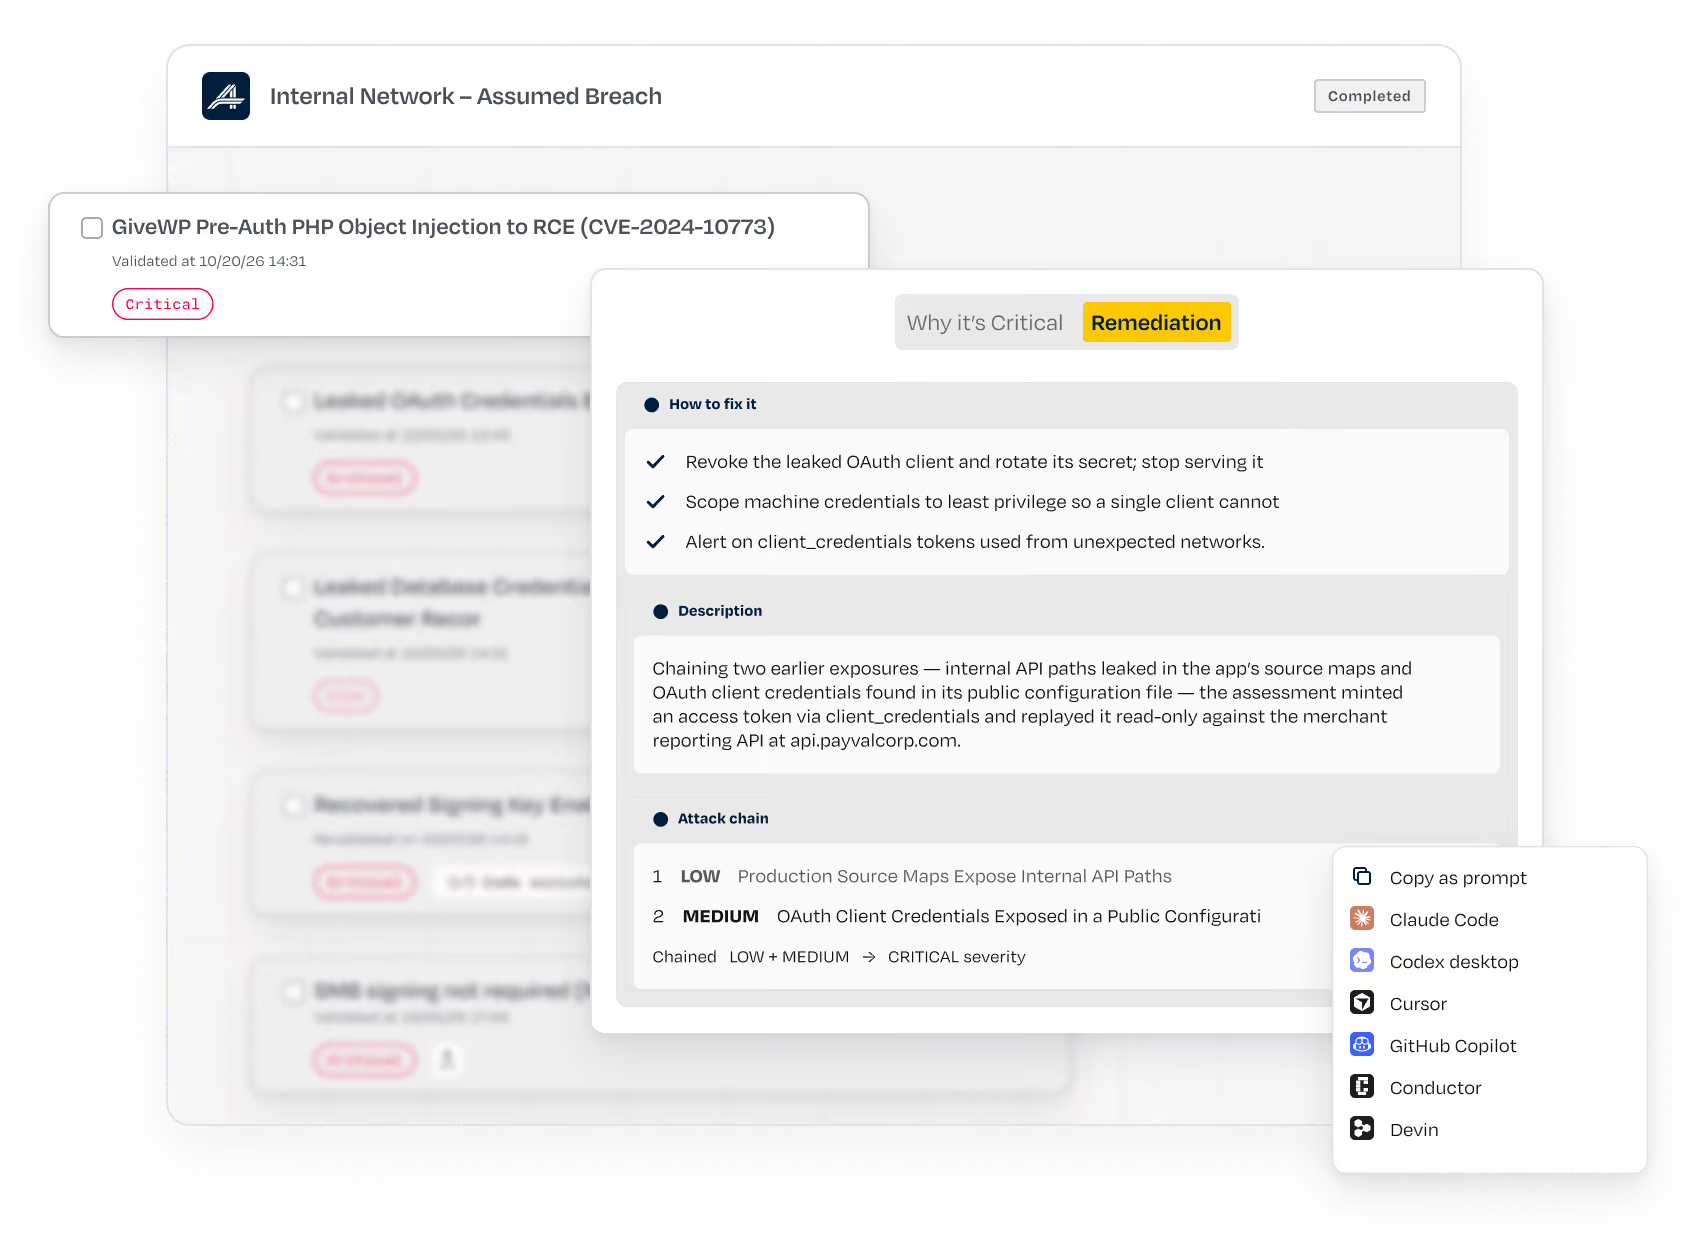
Remediate
Every proven path arrives with a fix. Send it to your ticketing system or coding agent, or route it to your WAF, cloud security and SIEM tools.
Get a demo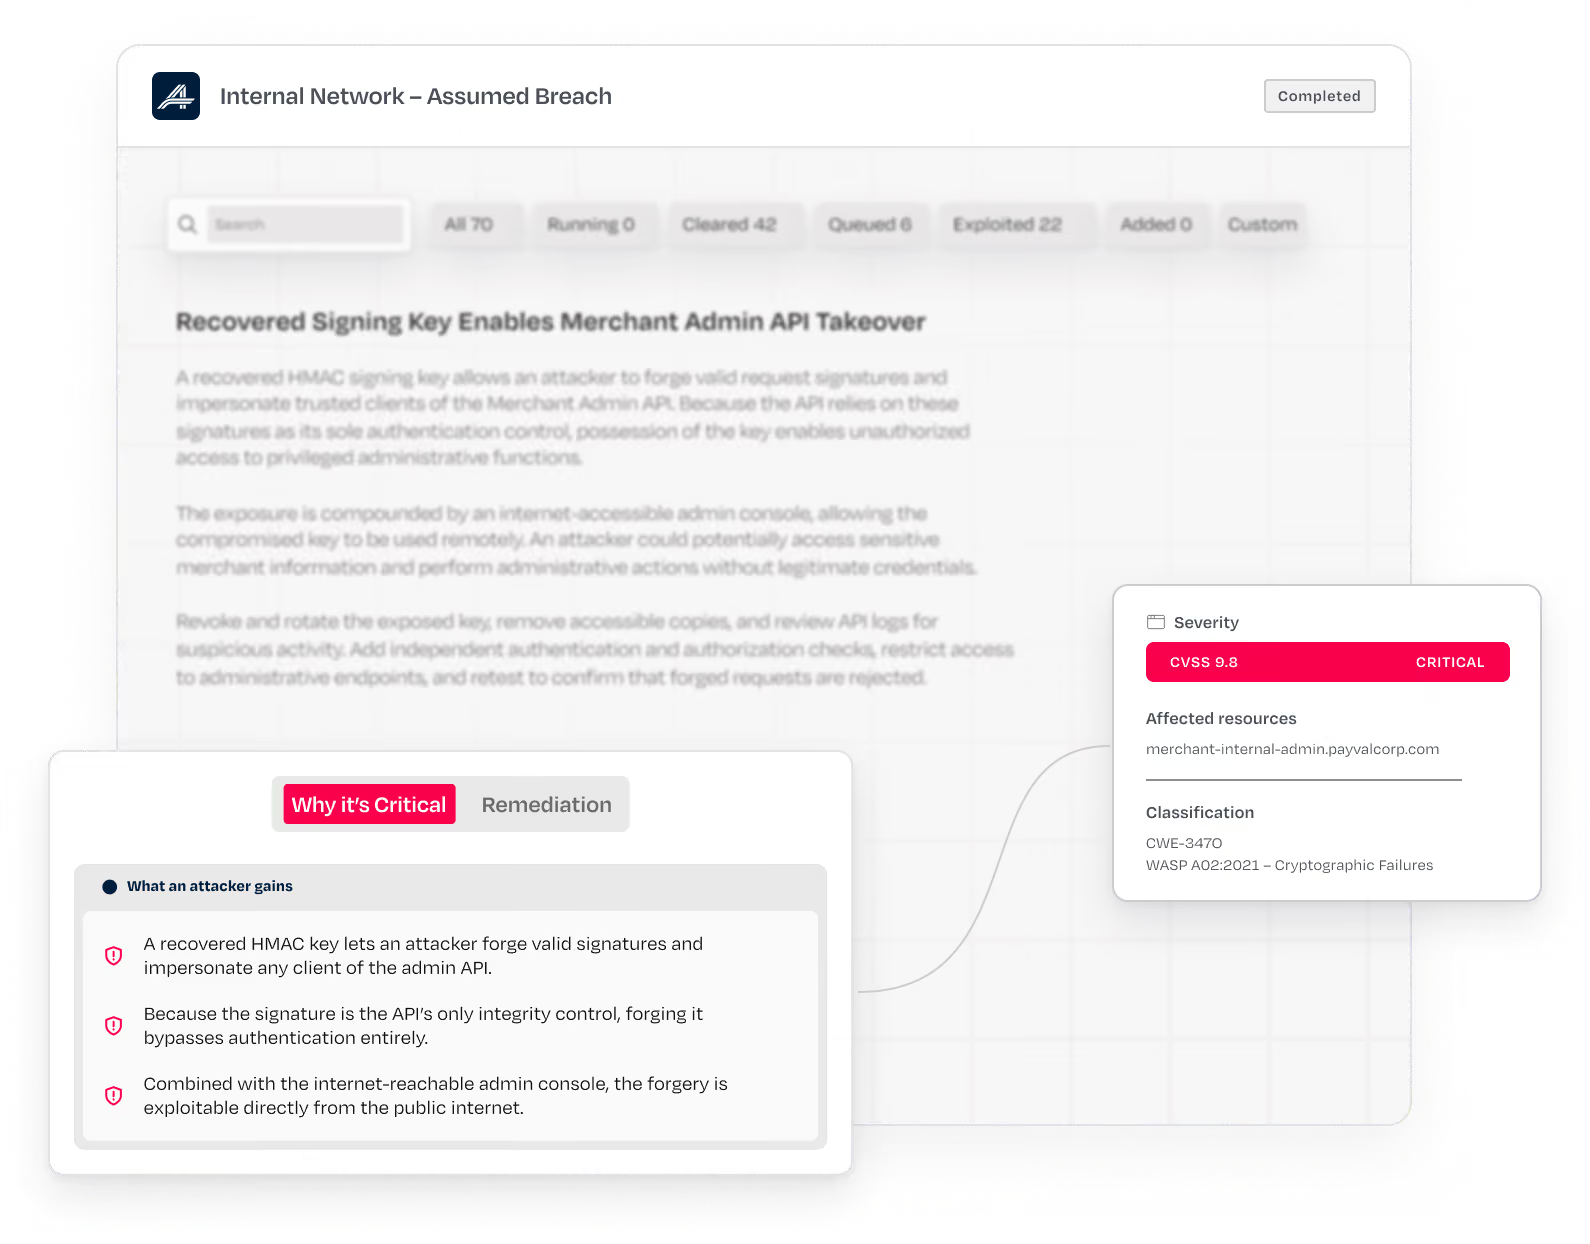
Retest
The agents retest the same path until it's confirmed closed. Each new test starts again from your domain, so a subsidiary, an acquisition or a system nobody registered gets found and attacked, and a fix that regresses gets caught.
Get a demo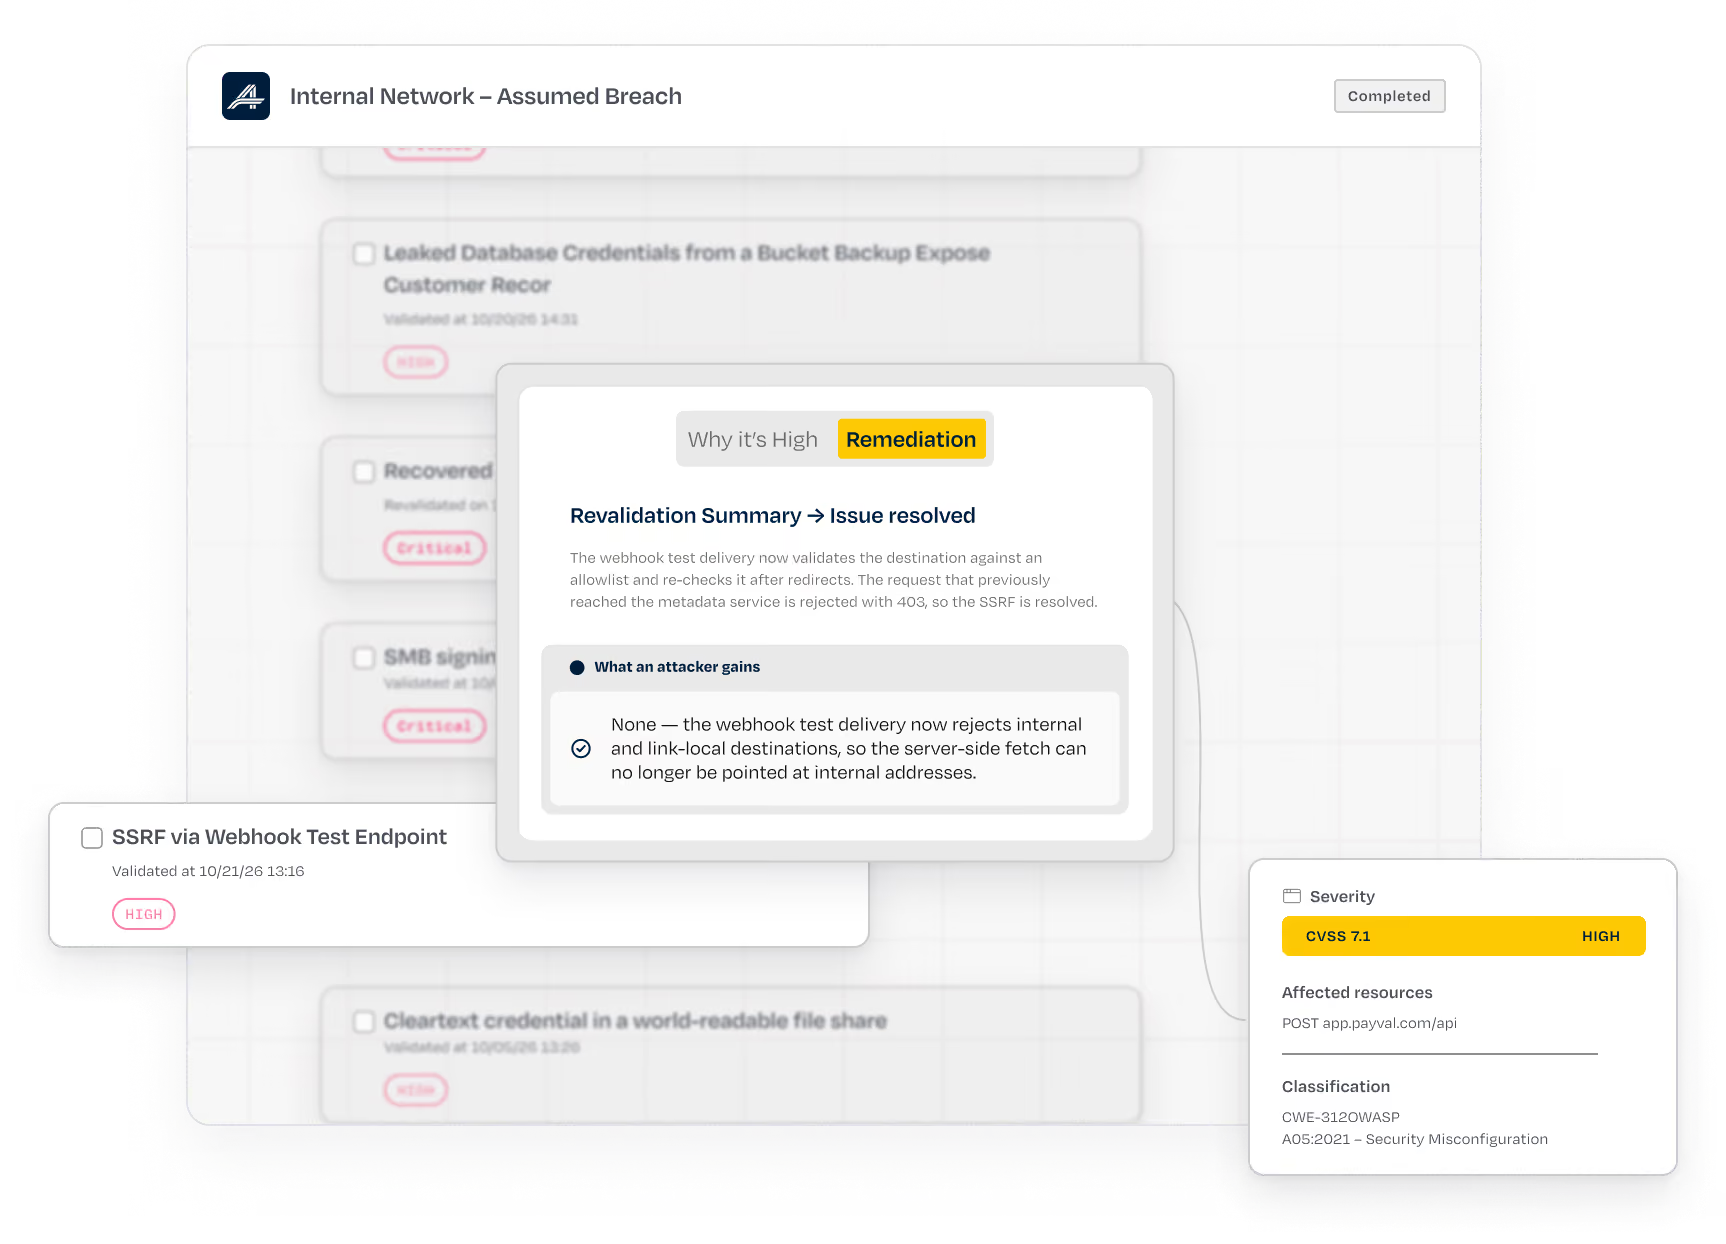
From a list of exposures to closed paths.
blast radius and a fix
domain and tested once you approve them
flaws with no published CVE
Behind every attack
The Harness
100+ specialized agents, orchestrated through one engine that selects the right AI model and validates every result.
Knowledge Graph
Attack paths, business context, fixes, and retests build a persistent intelligence layer that integrates with your SIEM and SOAR.
Apex-Domain Discovery
Find related root domains, subsidiaries and acquisitions, with evidence linking discovered assets to your organization.
Exposure-Class Testing
Web apps, exposed storage, mail servers and VPN gateways each get attacks built for that type of system.
Promote to a Full Test
Take a discovered web application into a full Web Apps test with credentials, from the same inventory.
Unsafe Output
Test for XSS, injected links and data leakage through rendered model output. Proof is validated in a real browser.
Fixes become a part of work
Findings go to the tools your team already uses, with the fix attached. Nothing to install. Run it as SaaS or in your own cloud account on AWS, Azure or Google Cloud, on AI models you've approved.


Attacks production without breaking it

Production-safe by default
Agents can’t write to your servers, leave anything behind, trigger purchases or emails, or knock a service offline.

Every lead reviewed first
Each exploitation task is checked against your safety policy before it runs.

An independent judge
Every action that changes state is intercepted and judged on its raw mechanics. No agent approves its own actions.

Shared memory
Every object created during a test is tracked across agents.

Hard scope limits
Anything outside your approved scope is blocked, whatever the agent decides.

Every intervention logged
Blocked actions can’t be retried with new wording, and every decision is logged for your auditors.
Questions, answered
Straight answers on how continuous
validation works in your environment.
See it. Prove it.
Close it.
Start with one domain. See the systems tied to your organization, the paths an attacker could use, and what it takes to close them.